
What Recruiters Look For: Cyber Security Analyst Resumes by Career Level
Hiring expectations shift significantly depending on your years of experience. Tailor your resume highlights to align directly with the seniority tier you are targeting:
Recruiters prioritize clean coding fundamentals, data structures, Git versioning, and demonstrated enthusiasm to learn modern frameworks.
- Lead with: Degree / CS coursework, active GitHub repositories, and capstone full-stack projects.
- Key proof: Functional API integrations, automated test suites, and clean documentation in pull requests.
- Red flag to avoid: Claiming to be an "expert" in 15 languages without demonstrable codebase history.
Recruiters seek independent feature ownership, database optimization, cloud deployments, and dependable agile delivery.
- Lead with: Quantified performance optimizations (latency reduction, API throughput, query tuning).
- Key proof: Production releases, microservices architecture, AWS/GCP infrastructure, and CI/CD pipelines.
- Red flag to avoid: Passive bullet points like "wrote code and fixed bugs" without citing technical scale or metrics.
Focus shifts from individual code output to high-level architecture decisions, mentoring engineers, and aligning tech with business KPIs.
- Lead with: Executive summary highlighting system scale, architectural strategy, and team mentorship.
- Key proof: High-availability distributed architectures (99.99% SLA), 25%+ cloud cost savings, and tech roadmaps.
- Red flag to avoid: Focusing strictly on low-level syntax while ignoring business ROI, team leadership, and cross-team influence.
How to Write an Interview-Winning Cyber Security Analyst Resume
Recruiters for cyber security analyst roles look for technical competence, proven delivery, and clean accountability. The most effective resumes balance technical proficiency with measurable operational outcomes:
1. The Professional Summary: Your 30-Second Pitch
Your summary should highlight your years of experience, core industry domain, and primary technical strengths.
2. Writing Realistic, Credible Bullet Points
Avoid writing passive duties like "Responsible for daily operations" or exaggerated claims. Focus on genuine scope and process ownership:
- Instead of: "Worked on daily projects and tasks."
Write: "Lead Tier 3 SOC threat hunting and digital forensics across an enterprise defense network protecting 45,000 endpoints and cloud environments." - Instead of: "Helped improve team procedures."
Write: "Configured Splunk SIEM correlation rules and automated SOAR playbooks, reducing average Mean Time to Detect (MTTD) from 4 hours to 12 minutes." - Instead of: "Communicated with clients and partners."
Write: "Coordinated containment and remediation of a sophisticated nation-state spear-phishing campaign, safeguarding proprietary defense contract data."
Copy-Paste Ready Resume Content
Click "Copy Text" to grab these pre-formatted sections and paste them into our AI Resume Builder or your own word processor:
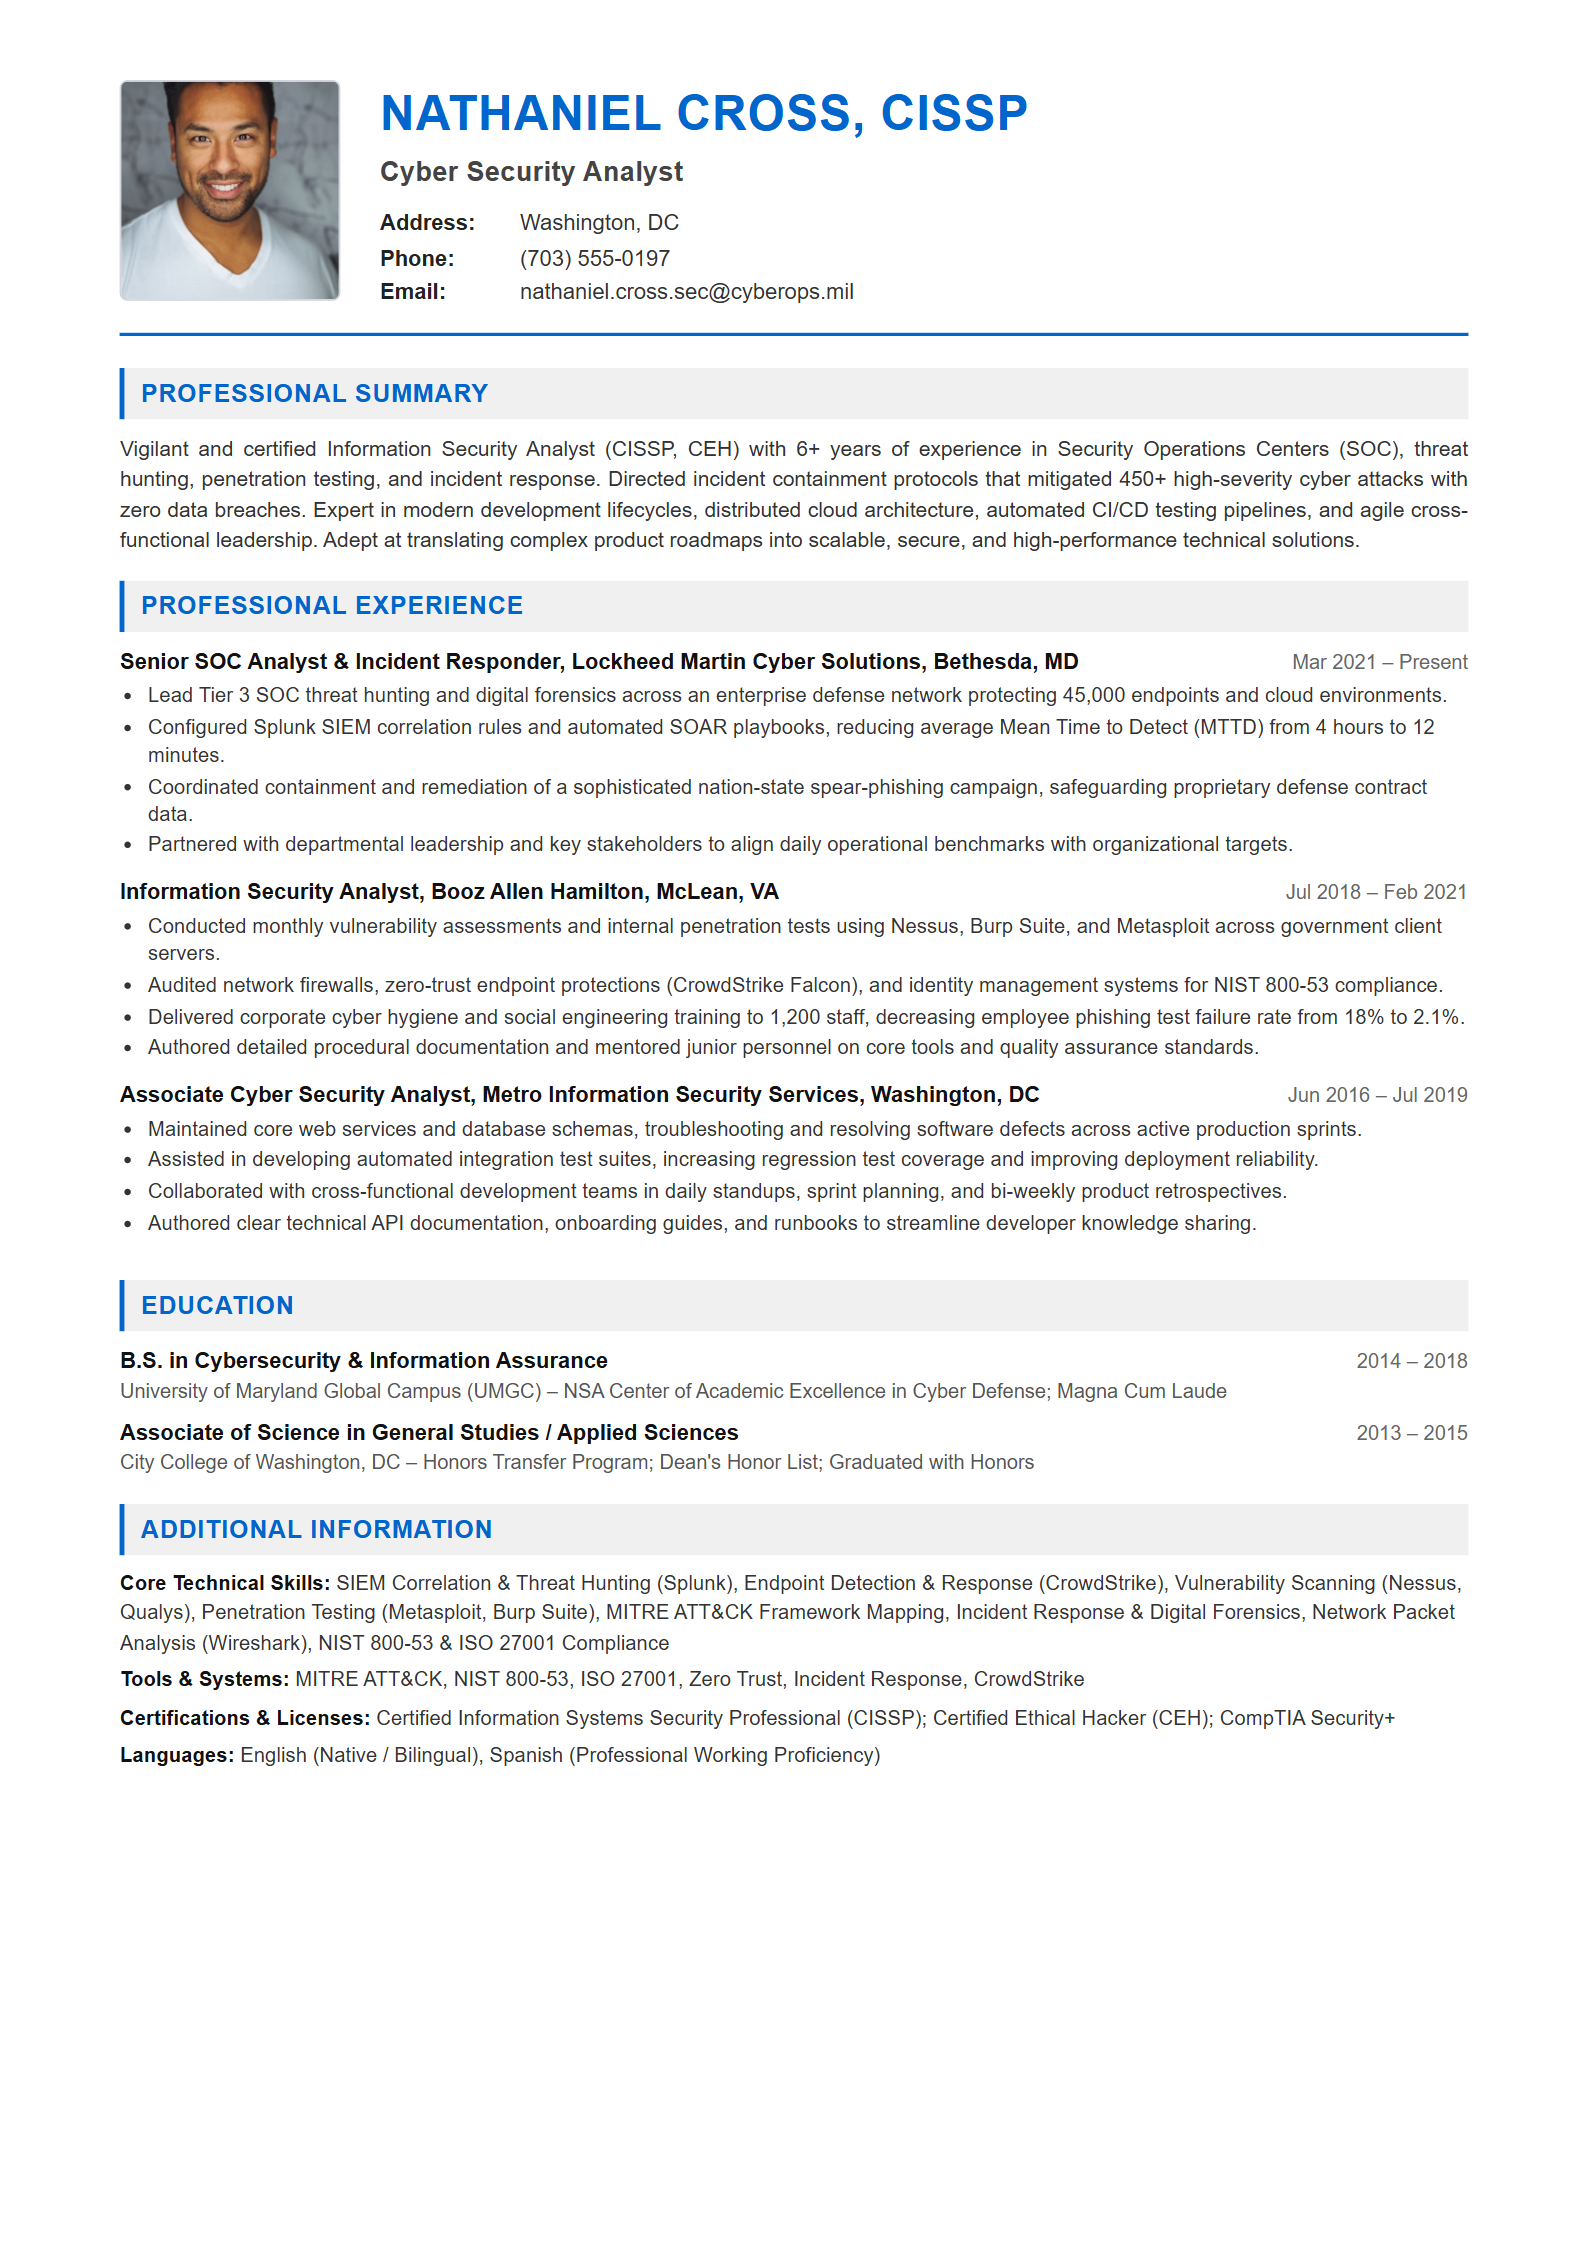
NATHANIEL CROSS, CISSP
Cyber Security Analyst
Address: Washington, DC
Phone: (703) 555-0197
Email: nathaniel.cross.sec@cyberops.mil

PROFESSIONAL SUMMARY
Vigilant and certified Information Security Analyst (CISSP, CEH) with 6+ years of experience in Security Operations Centers (SOC), threat hunting, penetration testing, and incident response. Directed incident containment protocols that mitigated 450+ high-severity cyber attacks with zero data breaches. Expert in modern development lifecycles, distributed cloud architecture, automated CI/CD testing pipelines, and agile cross-functional leadership. Adept at translating complex product roadmaps into scalable, secure, and high-performance technical solutions.
Senior SOC Analyst & Incident Responder | Lockheed Martin Cyber Solutions, Bethesda, MD
Mar 2021 – Present
• Lead Tier 3 SOC threat hunting and digital forensics across an enterprise defense network protecting 45,000 endpoints and cloud environments.
• Configured Splunk SIEM correlation rules and automated SOAR playbooks, reducing average Mean Time to Detect (MTTD) from 4 hours to 12 minutes.
• Coordinated containment and remediation of a sophisticated nation-state spear-phishing campaign, safeguarding proprietary defense contract data.
• Partnered with departmental leadership and key stakeholders to align daily operational benchmarks with organizational targets.

Information Security Analyst | Booz Allen Hamilton, McLean, VA
Jul 2018 – Feb 2021
• Conducted monthly vulnerability assessments and internal penetration tests using Nessus, Burp Suite, and Metasploit across government client servers.
• Audited network firewalls, zero-trust endpoint protections (CrowdStrike Falcon), and identity management systems for NIST 800-53 compliance.
• Delivered corporate cyber hygiene and social engineering training to 1,200 staff, decreasing employee phishing test failure rate from 18% to 2.1%.
• Authored detailed procedural documentation and mentored junior personnel on core tools and quality assurance standards.

Associate Cyber Security Analyst | Metro Information Security Services, Washington, DC
Jun 2016 – Jul 2019
• Maintained core web services and database schemas, troubleshooting and resolving software defects across active production sprints.
• Assisted in developing automated integration test suites, increasing regression test coverage and improving deployment reliability.
• Collaborated with cross-functional development teams in daily standups, sprint planning, and bi-weekly product retrospectives.
• Authored clear technical API documentation, onboarding guides, and runbooks to streamline developer knowledge sharing.
B.S. in Cybersecurity & Information Assurance
University of Maryland Global Campus (UMGC) | 2014 – 2018
University of Maryland Global Campus (UMGC) – NSA Center of Academic Excellence in Cyber Defense; Magna Cum Laude

Associate of Science in General Studies / Applied Sciences
City College of Washington, DC | 2013 – 2015
City College of Washington, DC – Honors Transfer Program; Dean's Honor List; Graduated with Honors
Core Technical Skills: SIEM Correlation & Threat Hunting (Splunk), Endpoint Detection & Response (CrowdStrike), Vulnerability Scanning (Nessus, Qualys), Penetration Testing (Metasploit, Burp Suite), MITRE ATT&CK Framework Mapping, Incident Response & Digital Forensics, Network Packet Analysis (Wireshark), NIST 800-53 & ISO 27001 Compliance
Tools & Systems: MITRE ATT&CK, NIST 800-53, ISO 27001, Zero Trust, Incident Response, CrowdStrike
Certifications & Licenses: Certified Information Systems Security Professional (CISSP); Certified Ethical Hacker (CEH); CompTIA Security+
Languages: English (Native / Bilingual), Spanish (Professional Working Proficiency)
Essential Cyber Security Analyst Keywords for 2026
Ensure your resume includes these core technical competencies and software systems to match recruiter search queries: